Policy is abstract
Frameworks rarely say what your architecture needs.
Enterprise AI needs governance built in—from policy to code. AIGovQ turns your use-case context into relevant governance checks, explains gaps and next steps, and provides a Governance Readiness Rating (GRR) during development.
Frameworks rarely say what your architecture needs.
Access, oversight, and data risks go unchecked in prototypes.
Fixes cost more once a system has users and integrations.
Product, risk, and compliance review different pictures.
Description or README
Policy-driven analysis
With reasons and next steps
Priorities and flagged gaps
Informed by the EU AI Act, GDPR, NIST AI RMF, ISO/IEC 42001, Singapore's Model AI Governance Framework, and OWASP LLM and agent guidance. Readiness guidance only; not legal advice, certification, or a guarantee of compliance.
Plan early with reasoned recommendations, then measure readiness once the system takes shape.
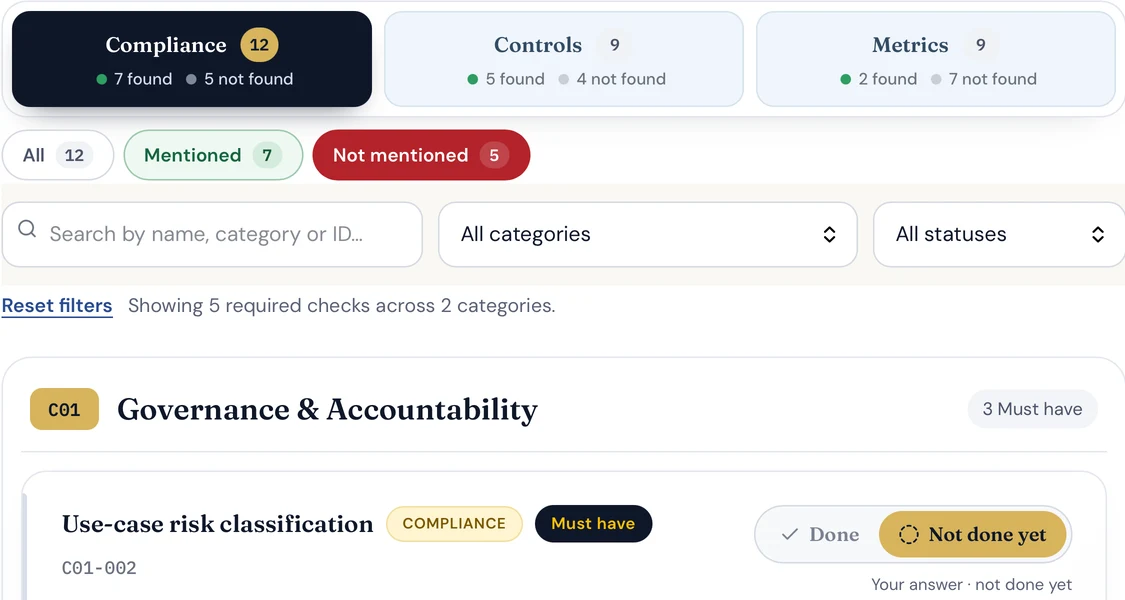
Plan governance from the start with recommended compliance checks, controls and metrics—and why they matter for your PoC or development.
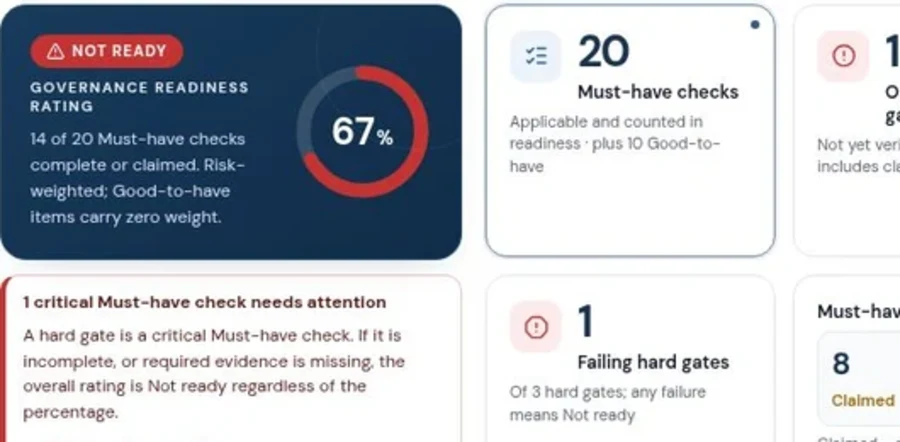
Get your Governance Readiness Rating (GRR), identify governance gaps, and prioritize actions for further implementation.
GRR reflects the governance readiness of your AI use case, helping teams identify gaps, prioritize actions, and understand what to implement to address applicable AI governance requirements.
AI identifies relevant governance requirements and gaps from your use-case description or documents.
Stated implementation receives full credit; documented plans receive 75% planning credit, not completed coverage. Missing information receives zero, and critical safeguards must be implemented.
The readiness rating is based on applicable Must-have checks across governance categories. Categories more relevant to the use case’s risks carry greater weight. Good-to-have recommendations do not affect the rating.
An unmet critical safeguard prevents a Ready rating, even when other coverage is strong.
Pre-development: recommendations only, no GRR.
Incomplete context: GRR is provisional and based only on what you supply. Missing information is declared, not treated as confirmed absence.
For a more comprehensive review: upload a use-case or model risk management (MRM) document. If unavailable, provide a README with supporting plans or references covering the use-case purpose and owner, risk and data classification, data sources and handling, governance safeguards, and output evaluation and testing plans. You can upload multiple documents together to provide this context.
What it is not: a measure of output quality or runtime performance, a legal certification, or an AI use-case validation or evaluation score.
Type, upload, or continue with limited context. No follow-up questionnaire.
See applicable checks, their rationale, and highlighted information gaps.
Download your report and follow prioritized next steps.
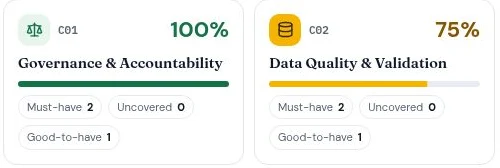
Category-level percentages bring strengths and gaps into focus, so teams can plan their next steps.
Turn AI governance from a late-stage hurdle into a design input. Find gaps while they are still easy to fix.
Get startedGuidance, not certification. Not legal advice or a guarantee of compliance.