Policy is abstract
Frameworks rarely say what your architecture needs.
Enterprise AI needs governance built in—from policy to code. AIGovQ is an AI governance assessment tool for your use case: it selects relevant checks, highlights priority gaps and practical next steps, and provides a Governance Readiness Rating (GRR) during development.
Frameworks rarely say what your architecture needs.
Access, oversight, and data risks go unchecked in prototypes.
Fixes cost more once a system has users and integrations.
Product, risk, and compliance review different pictures.
Review a GenAI, RAG or AI agent use case against relevant governance requirements, controls and metrics—not a generic company-wide maturity questionnaire.
Description or README
Policy-driven analysis
With reasons and next steps
Priorities and flagged gaps
Informed by the EU AI Act, GDPR, NIST AI RMF, ISO/IEC 42001, Singapore's Model AI Governance Framework, and OWASP LLM and agent guidance. Readiness guidance only; not legal advice, certification, or a guarantee of compliance.
Plan early with reasoned recommendations, then measure readiness once the system takes shape.
Plan governance from the start with recommended compliance checks, controls and metrics—and why they matter for your PoC or development.
Get your Governance Readiness Rating (GRR), identify governance gaps, and prioritize actions for further implementation.
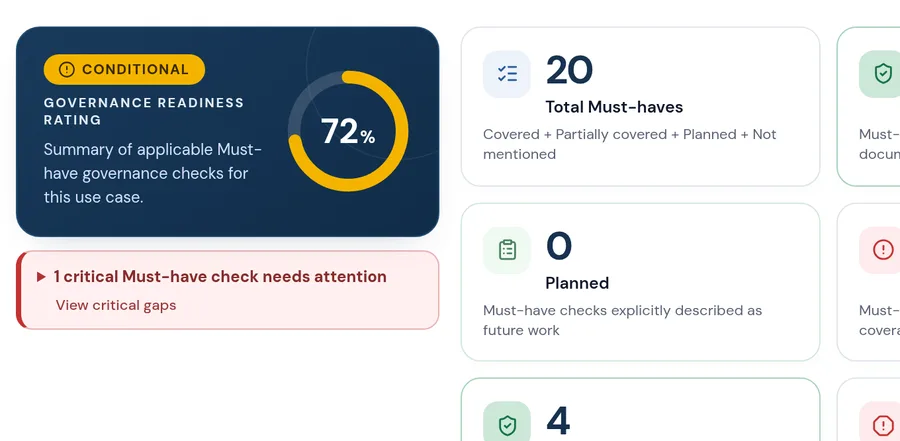
GRR reflects the governance readiness of your AI use case, helping teams identify gaps, prioritize actions, and understand what to implement to address applicable AI governance requirements.
AI identifies relevant governance requirements and gaps from your use-case description or documents.
Stated coverage receives full credit; partial coverage receives 90% and explicit documented plans receive 85%. Not mentioned receives zero. Critical flags highlight attention without an additional rating penalty.
GRR starts with applicable Must-have checks, weighted by the use case’s risks. Covered, partially covered and planned Recommended checks receive proportional extra recognition. Critical safeguards are highlighted for attention, without a separate rating penalty or bonus.
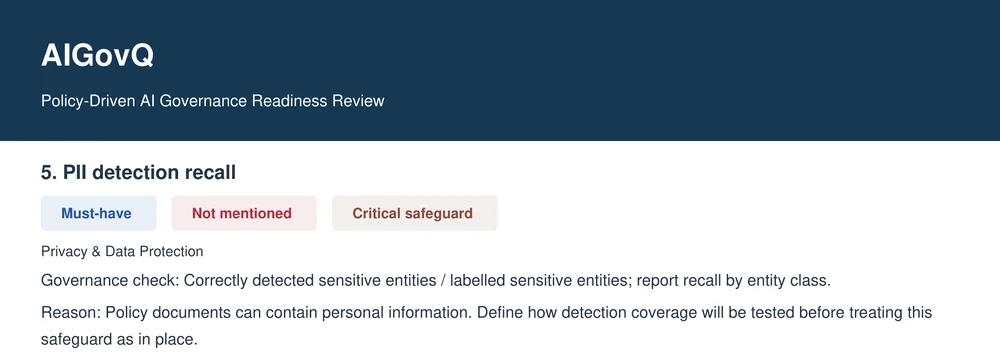
Important governance gaps stay visible alongside the calculated GRR, helping teams decide what to address next.
Pre-development: recommendations only, no GRR.
Incomplete context: GRR is provisional and based only on what you supply. Missing information is declared, not treated as confirmed absence.
For a more comprehensive review: upload a use-case or model risk management (MRM) document. If unavailable, provide a README with supporting plans or references covering the use-case purpose and owner, risk and data classification, data sources and handling, governance safeguards, and output evaluation and testing plans. You can upload multiple documents together to provide this context.
What it is not: a measure of output quality or runtime performance, a legal certification, or an AI use-case validation or evaluation score.
Type, upload, or continue with limited context. No follow-up questionnaire.
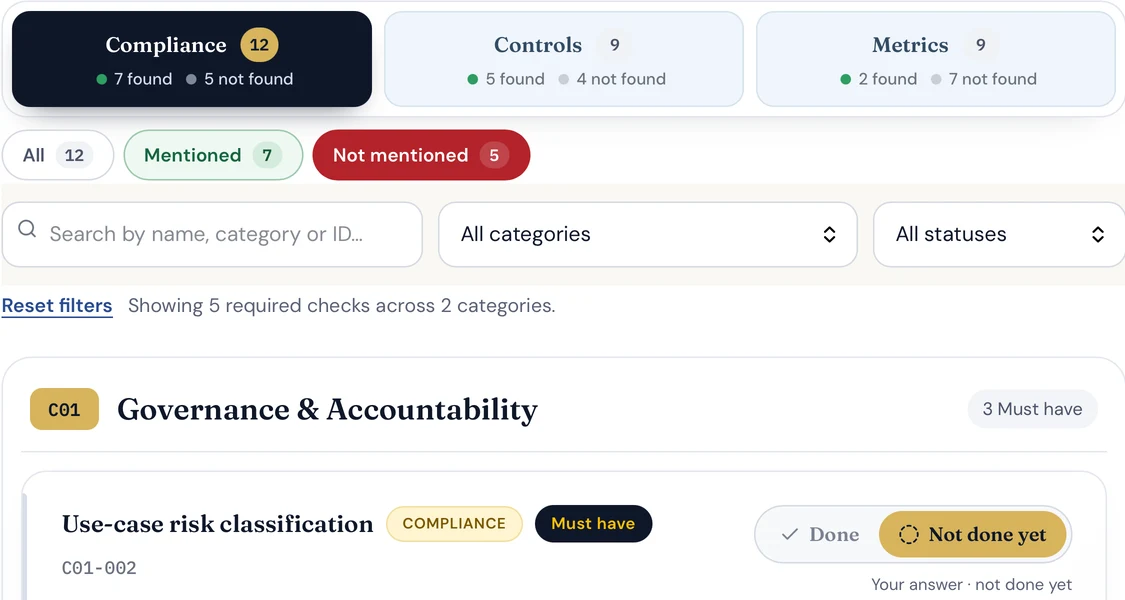
See applicable checks, their rationale, and highlighted information gaps.
Download your report and follow prioritized next steps.
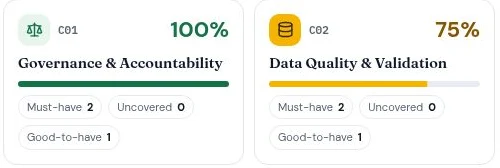
Category-level percentages bring strengths and gaps into focus, so teams can plan their next steps.
Turn AI governance from a late-stage hurdle into a design input. Find gaps while they are still easy to fix.
Get startedGuidance, not certification. Not legal advice or a guarantee of compliance.